Blog
Your AI Bill Spiked. Here's How to Find Out Exactly Why.
Published on Sep 1, 2026 • 14 min read

Featured Articles
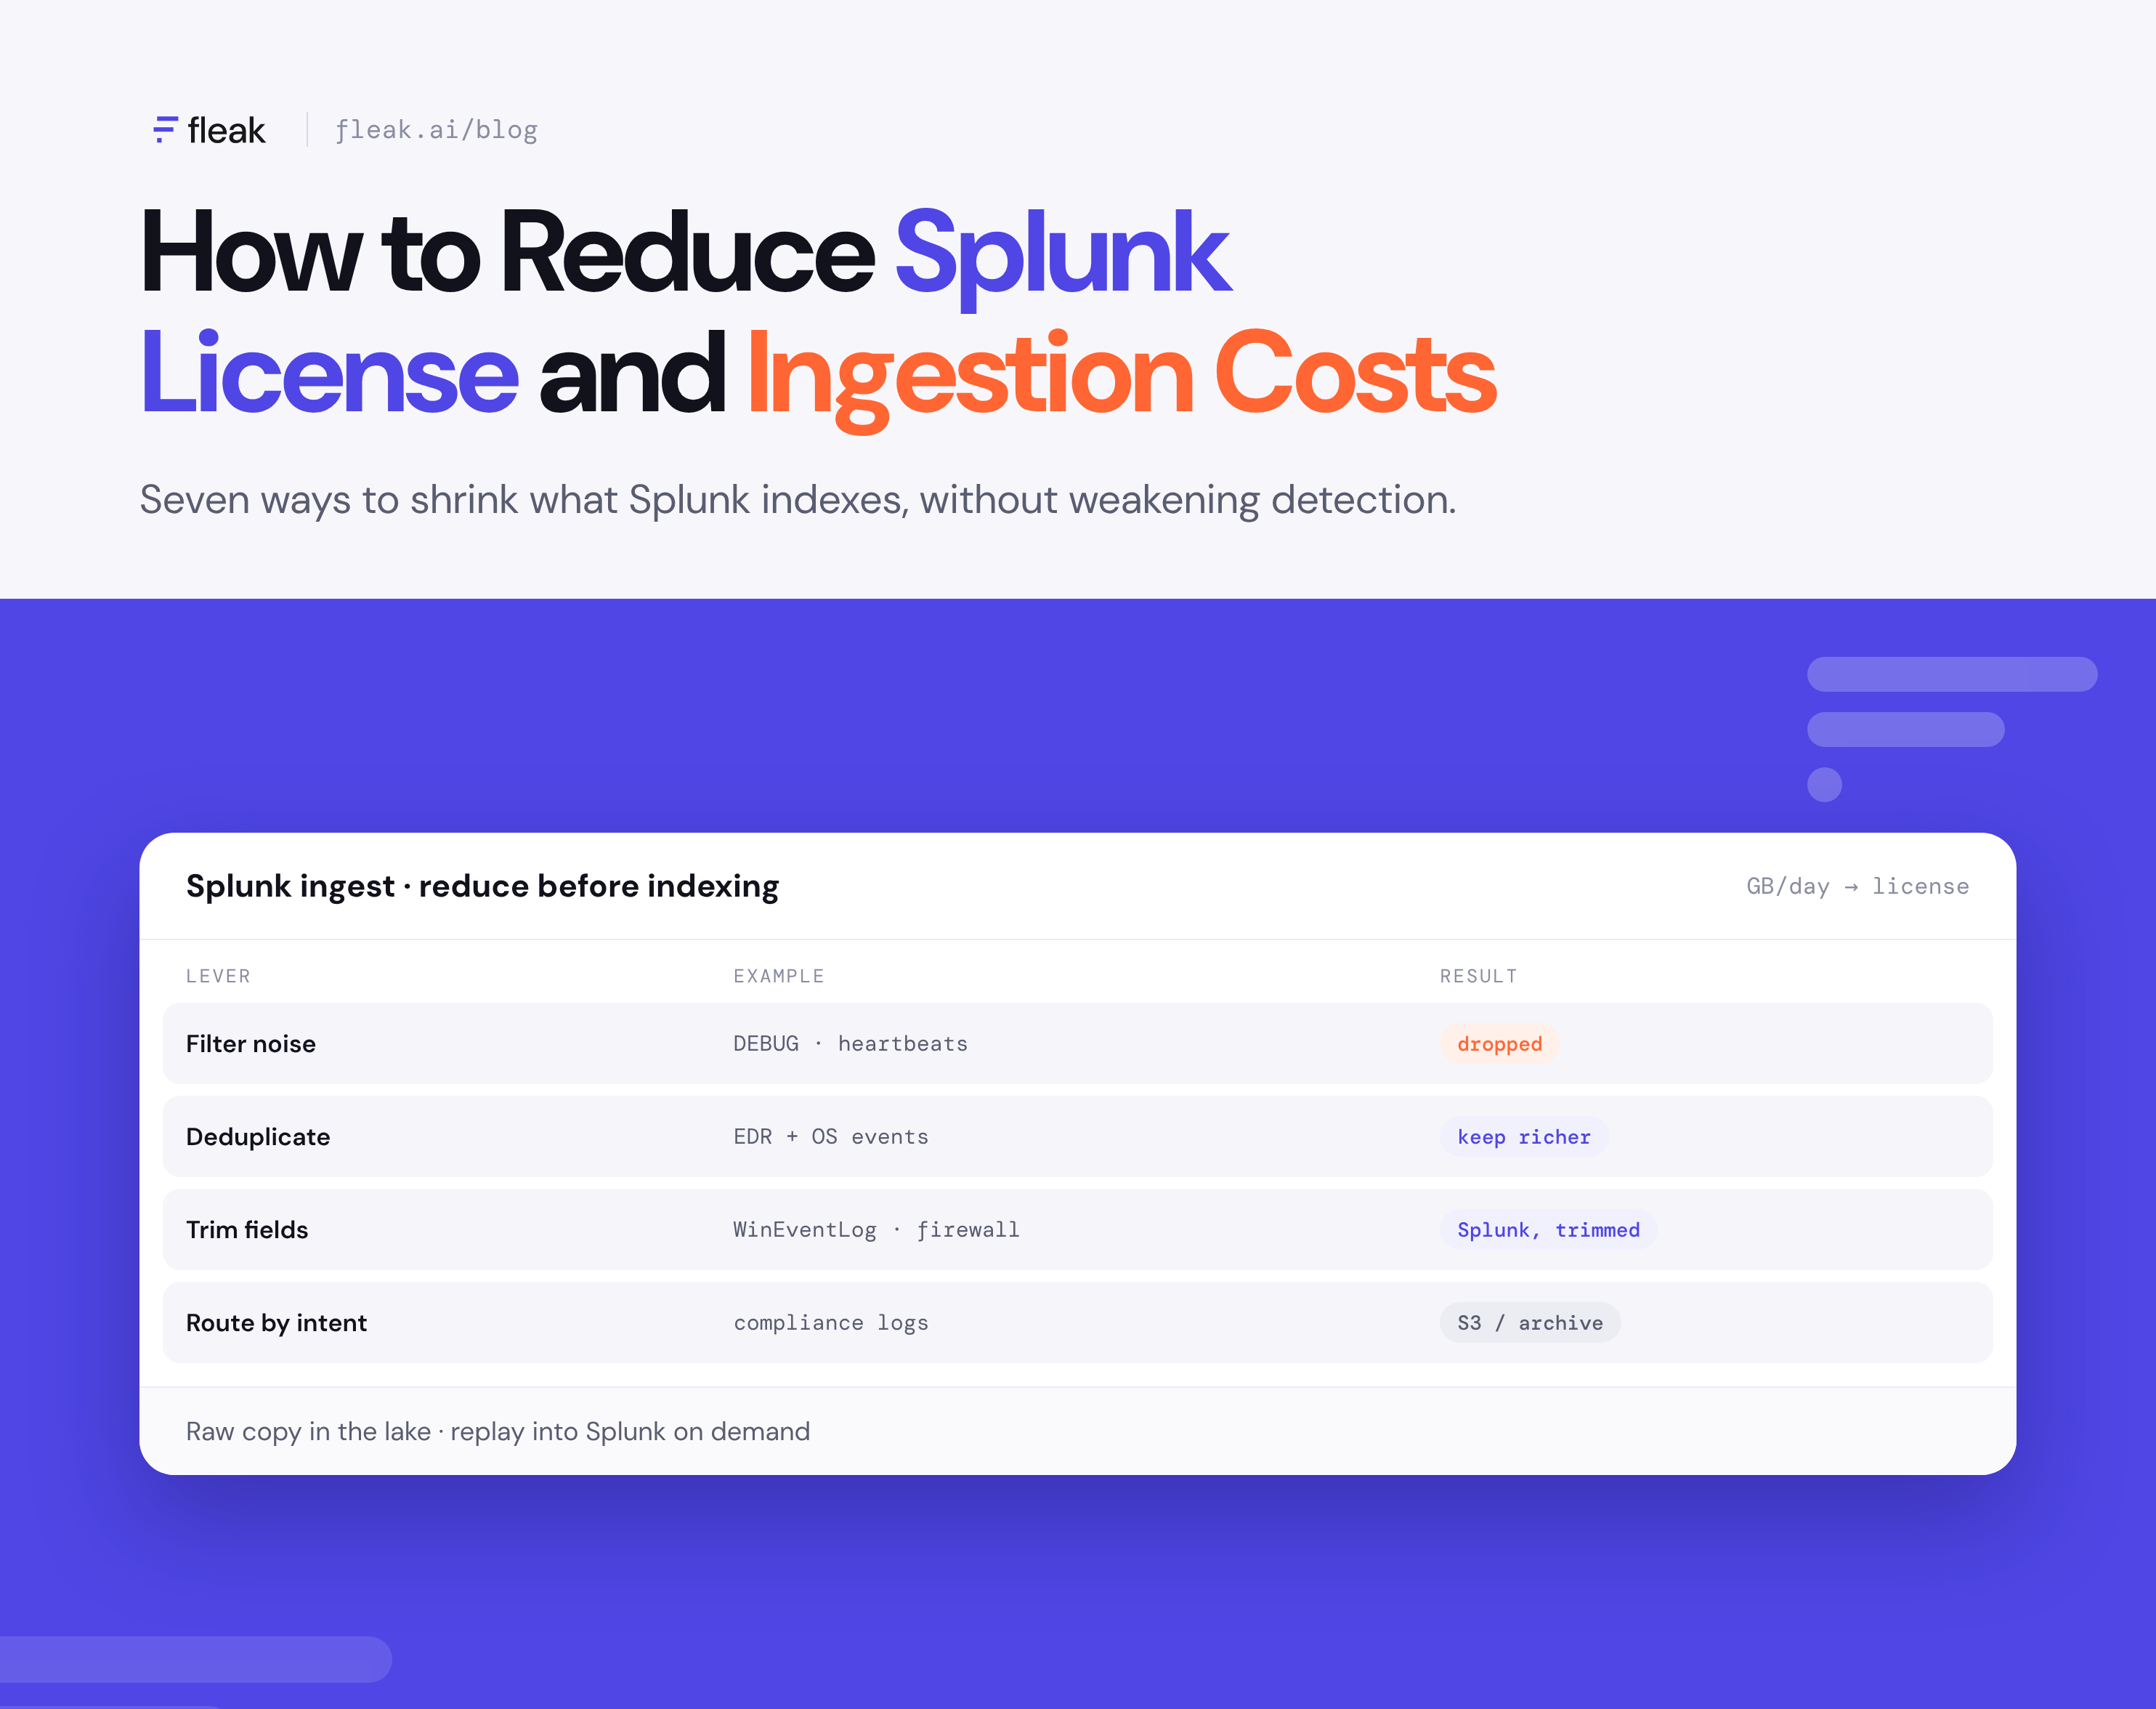
How to Reduce Splunk License and Ingestion Costs
A practical guide to SIEM cost reduction. Learn what drives Splunk license and ingestion costs and seven ways to cut them without weakening detection.
Nov 6, 2026 • 8 min read
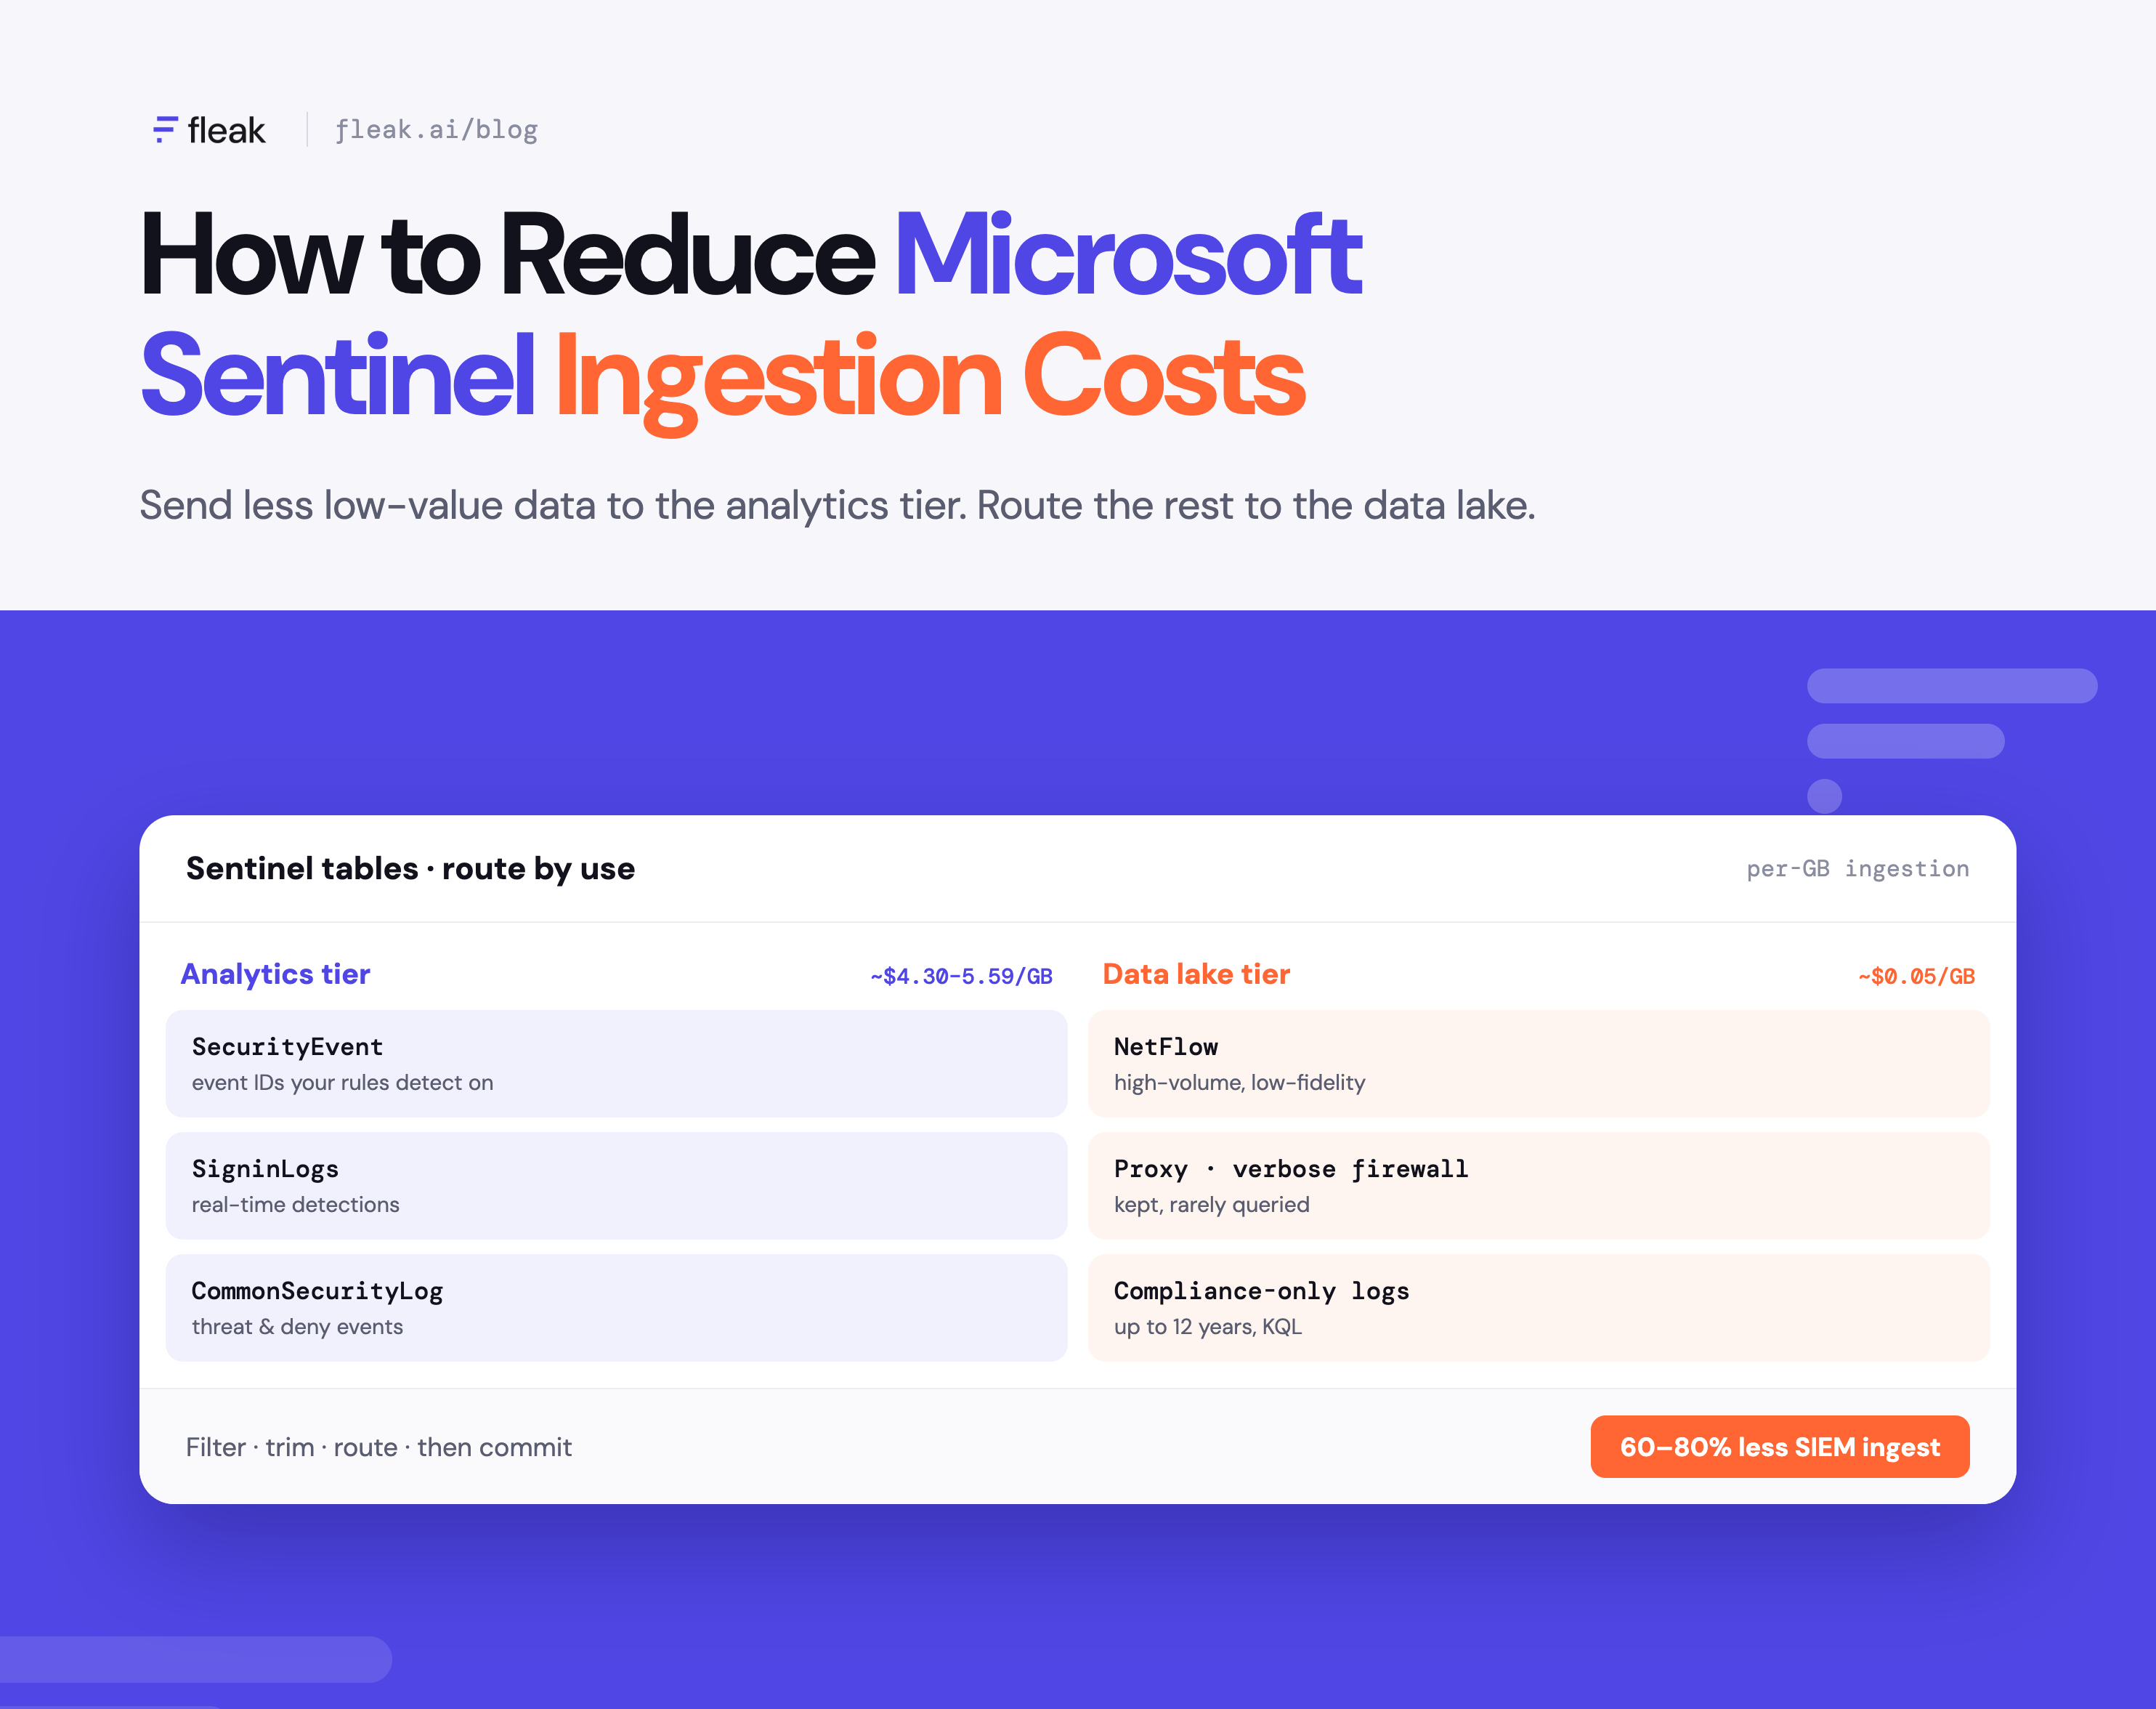
How to Reduce Microsoft Sentinel Ingestion Costs
Cut Microsoft Sentinel costs by sending less low-value data to the analytics tier: filter before ingestion, route secondary logs to the data lake, claim free sources and size your commitment tier last.
Nov 4, 2026 • 8 min read
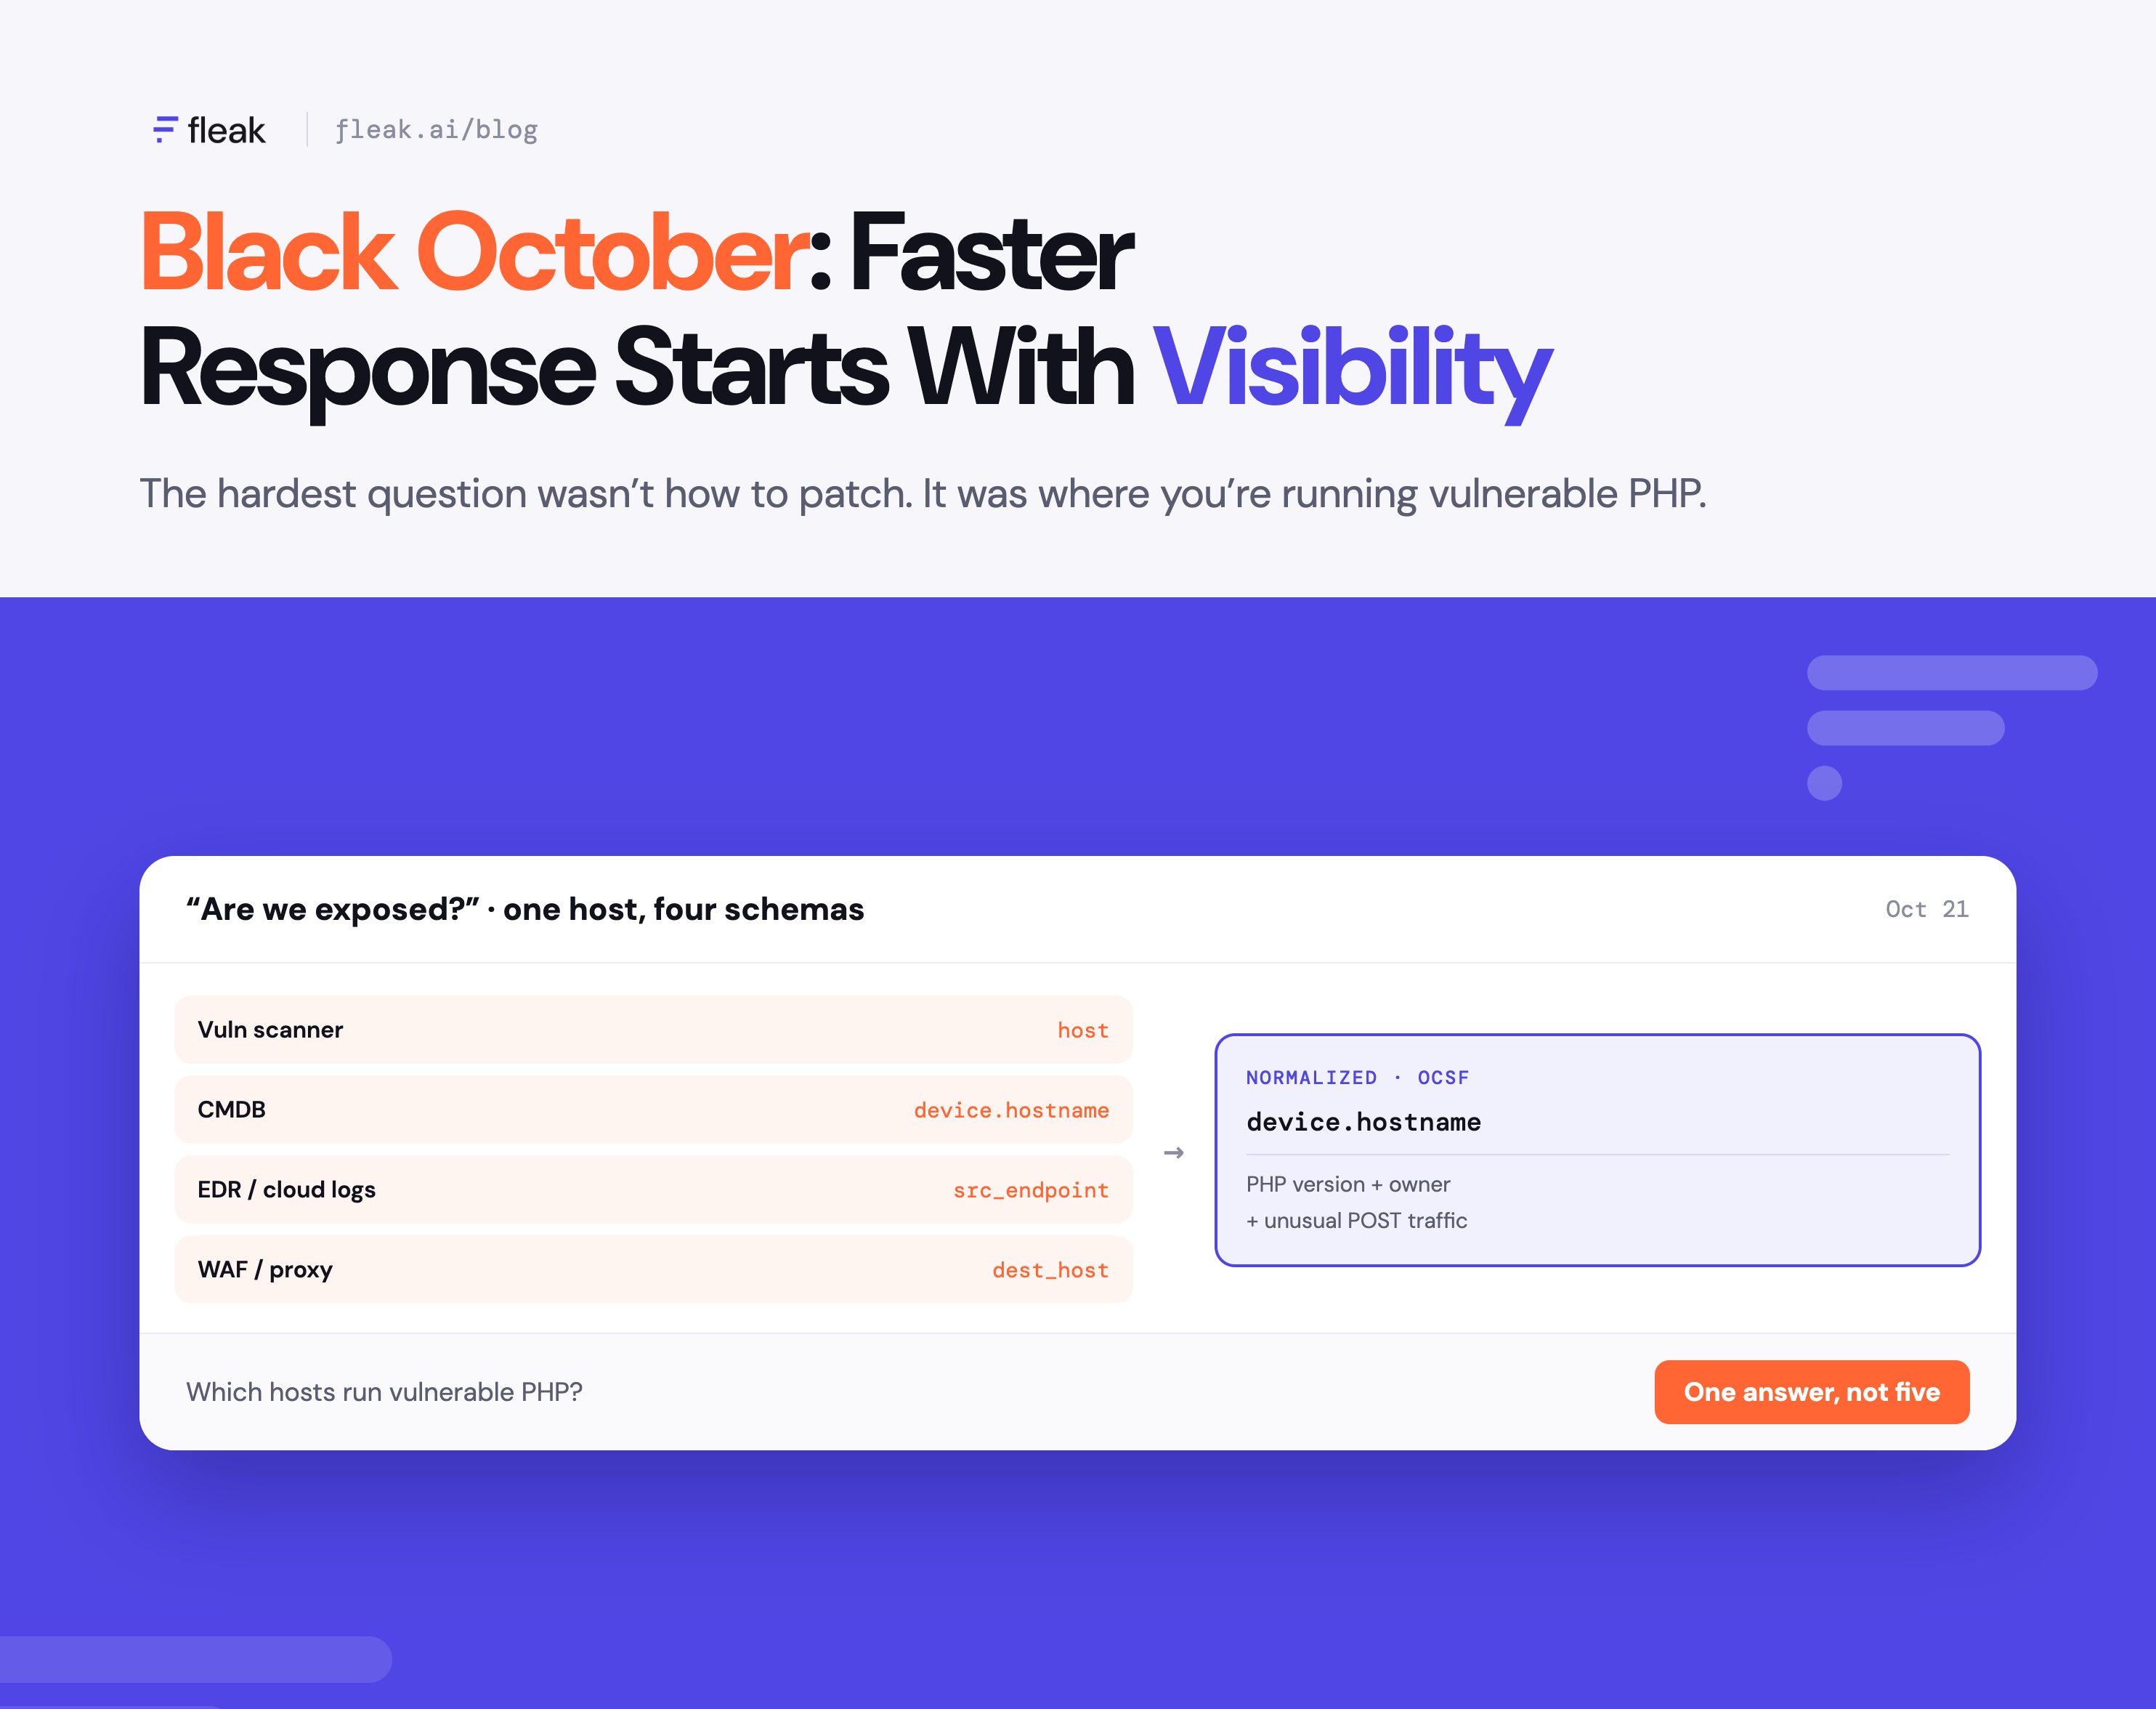
Black October: Faster Response Starts With Visibility
What the Black October PHP vulnerabilities taught security teams about response time, vulnerability visibility and why normalized data comes first.
Nov 2, 2026 • 8 min read
Oct 27, 2026 • 12 min read
From Cribl Lake to Splunk Machine Data Lake: Move Your History Without Losing Detections

Oct 26, 2026 • 10 min read
PHP2Shell (CVE-2026-109618): How MSPs Can Triage Exposed Clients Fast
Oct 21, 2026 • 9 min read
How to Reduce Google SecOps Costs Before Your Credits Run Out
Oct 19, 2026 • 11 min read
How Much of My SIEM Data Do Detection Rules Actually Use? What We Learned From CloudTrail
Oct 13, 2026 • 6 min read
The Noise Tax: Why Most SIEM Spend Goes to Data That Never Triggers a Detection
Oct 9, 2026 • 11 min read
How to Explain SIEM Costs to Your CFO Without Losing the Security Budget
Oct 6, 2026 • 8 min read
Fleak vs. Cribl: A Total Cost of Ownership Comparison
Oct 5, 2026 • 8 min read
Data Mapping vs. Schema Mapping: What's the Difference?
Oct 2, 2026 • 6 min read
What Is Schema Mapping in Security and Observability Data Pipelines?
Bring us your messiest data.
30 minutes. Bring your messiest data source.